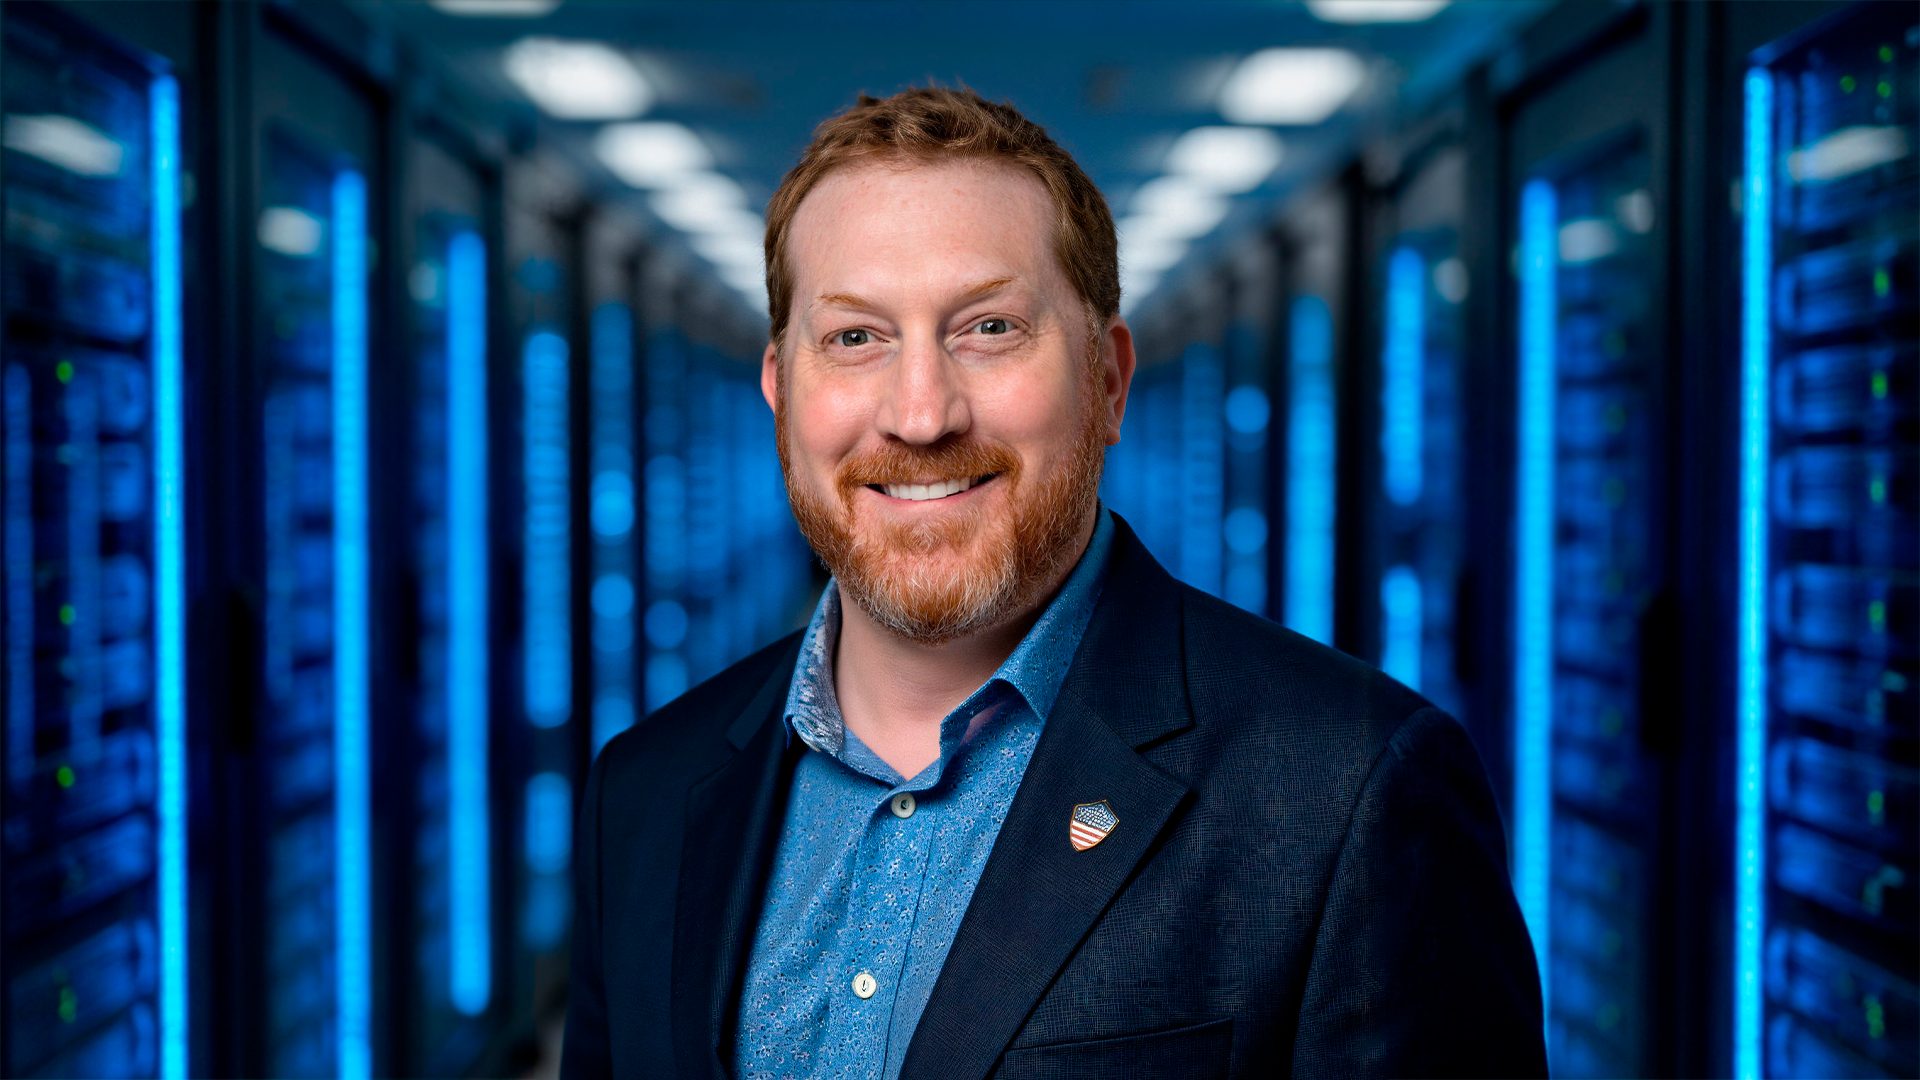

Every board that approves an AI policy walks out of the room believing it has done the governing. It has not. It has produced a statement of intent, and intent has never stopped anyone from doing anything. The gap between a signed document and a running system is where organizations are quietly accumulating risk right now, and the gap is widening because agents are arriving faster than the controls meant to hold them. Jim Tunnessen, who spent two decades in federal technology leadership and now works on agent governance at GOVERNBOX.ai, argues that the question is not whether a policy exists but whether anything between a person and a model enforces it. His framing is blunt: “If you can, the policy is governing. If you can’t, the policy is decorating.”
The Five Questions An Auditor Will Ask
Tunnessen tests governance with five questions applied to every AI system in production:
- Who owns it?
- What data does it touch?
- How was it tested?
- How is it monitored?
- What happens when it fails?
The order matters. Ownership comes first because a policy that fails to name a human on every system is unenforceable by construction. “When it breaks, there’s nobody to call,” he says, and that single omission collapses the rest of the structure regardless of how carefully the document was drafted.
What makes the test uncomfortable is that it is not hypothetical. “An auditor doesn’t ask whether you have a policy. Neither does a regulator, and neither will an attorney general,” Tunnessen says. “They ask you to prove those five things for a specific system on a specific date.” Most organizations can produce the policy in seconds but not the proof. That asymmetry is the real exposure, because the ability to answer on demand, for a named system, on a named date, is what separates a governance program from a filing cabinet.
Where The Document And The System Come Apart
Separation begins at the first change nobody thought required re-approval. Tunnessen traces the flaw to an inherited assumption from federal practice, where an authority to operate is a point-in-time judgment: on this date, this system, as configured, is acceptable. AI systems do not wait for that. A model version, a prompt, a set of connected data sources, and a list of permitted tools each change on separate schedules, owned by different people, and most of those people sit outside the organization. The vendor updates the model. Someone adds a data source. “The system you authorized is still running, still supposedly authorized by you, but it is a derivative,” he says. “What’s running is that system’s grandchild.”
The second fracture is the feature nobody procured. A policy governs the tools that staff choose, but has nothing to say about AI capabilities that a vendor switches on inside software the company already licensed. Tunnessen points to Microsoft and Google as the obvious cases: organizations that had planned a deliberate rollout with testing and training found themselves moving on the vendor’s timeline instead, working backward from a capability functioning live in the environment. The third fracture is the human in the loop, the clause every policy contains. “Watch the person,” he says. “If they approve at the speed the system produces, you have a rubber stamp with a job title.” Regulators have noticed. Rules now being drafted for automated decisions define meaningful human review as someone with genuine authority to override, not someone positioned to click approve.
Controls That Run Whether Anyone Is Watching
Tunnessen’s answer is a four-layer structure he calls the Agentic Control Plane, and each layer converts a sentence in the policy into something that executes on its own:
- Zero-trust agent identity comes first: every agent and automated caller gets its own credential, least-privilege scopes, and a named human owner, with no shared service accounts. His rule is unsentimental. “If you can’t revoke it in under a minute, you don’t govern it.”
- Orchestration moves the policy’s rules to the boundary where an agent calls a tool or a system of record, evaluating permitted tools, spending limits, and escalation conditions at the moment of action rather than in a quarterly review.
- Immutable infrastructure treats the model, prompt, and tool configuration as one versioned unit, so a change is a new version passing the same gate as the original. On a federal compliance agent, that gate was a golden test set the agent had to clear in the deployment pipeline, with schema-checked, tamper-sealed output so an approved answer could not be quietly edited later.
- Provenance closes the loop, letting outputs trace to sources.
Under all four sits an append-only log. “Governance is enforceable when a policy is a documented runtime decision with a receipt.”
Closing the maturity gap, he argues, is a question of friction rather than paperwork. Deloitte puts mature agentic governance at 21 percent of enterprises, self-reported and therefore generous, while roughly three-quarters of the same leaders expect to run agents at least moderately within the year. Longer policies and larger committees do not move that. Three moves do:
- Build the inventory with a named owner on every agent and AI-enabled system, including the ones a vendor switched on.
- Give every agent its own credential and make registration the only route to obtaining one.
- Run the full loop on one real agent before scaling, including rehearsing the failure.
“When the registered path takes ten minutes and the unregistered path doesn’t work, you get compliance without a memo.” Most organizations already own the raw materials, since zero trust, identity management, change control, and incident response all apply once an agent is understood as a new class of principal inside systems already governed.
Control, in his reading, does not mean approving every action. “That’s not control, that’s a bottleneck, and it fails the first week.” Having come up as a marine infantryman, Tunnessen reaches for commander’s intent and rules of engagement: give the unit the mission, the left and right limits, the conditions for stopping and calling back, then verify afterward that the limits held. Translated into systems, this means five things built before agents arrive:
- An agent registry where every agent is a first-class principal with an owner, a scope, and a kill switch.
- A control point between agents and systems of record where permitted tools, spending limits and human-approval triggers are enforced on every call.
- An append-only, replayable log with provenance.
- Drift detection comparing the approved baseline against what is running, with the machine flagging differences and never overwriting the human’s baseline.
- A human-review queue carrying real override authority, because Colorado, California, and the European Union are converging on the same four requirements for decisions about people: notice, explanation, meaningful human review, and producible records.
Leaders who build those five can let agents run because they can prove the envelope held. Leaders who do not will freeze or get surprised. “Control isn’t the brake,” Tunnessen says. “It’s what lets you go fast.”
Follow Jim Tunnessen on LinkedIn for more insights on AI governance, agent identity, and enforceable controls for autonomous systems.